
A command like `sudo -u nobody id -un` runs as a different user than `sudo id -u`, even though both start the same way. I kept digging into what decides whether either request is allowed.
That distinction helps you match sudo’s command form to the identity your task needs. The answer comes down to what sudo authorizes for your account.
What sudo authorizes
sudo runs a command as another user when the active security policy permits it. Without an explicit target, that user is root, but sudo does not turn your account into root or bypass the policy.
The policy checks the account that invoked sudo, the requested target identity, the host and the command. The default policy reads rules from sudoers, which administrators can manage with sudoers access rules.
| Form | What runs |
|---|---|
| sudo -n id -u | One permitted command as root by default |
| sudo -n -u nobody id -un | One permitted command as the named user |
| sudo -n -i — id -un | A login shell for the target user |
| sudo -n -s — sh -c ‘id -un’ | A shell using the current environment, subject to policy |
Check access and authentication
Run the list form to see which commands the policy allows your account to run. The exact output depends on the machine’s rules.
sudo -n -l
The non-interactive flag tells sudo not to ask for a password. If authentication would be required, the command fails instead of waiting for input. Without that flag, sudo may ask for your account password, use another configured authentication method, or proceed without a prompt when policy permits it.
Authentication caching is controlled by the policy and may let later commands run without another prompt for a configured interval. That does not grant new commands: authorization is checked for each request. If sudo reports that your account is not allowed, ask an administrator to review the rules rather than switching to an unrelated account.
Run a command with sudo
Put sudo before the command that needs elevated access. This harmless identity check prints the effective user ID and gives you a visible confirmation of the selected identity.
- Run the exact command below. The non-interactive option makes it stop if a password prompt would be needed.
- Read the output. The value 0 is the user ID reserved for root.
sudo -n id -u
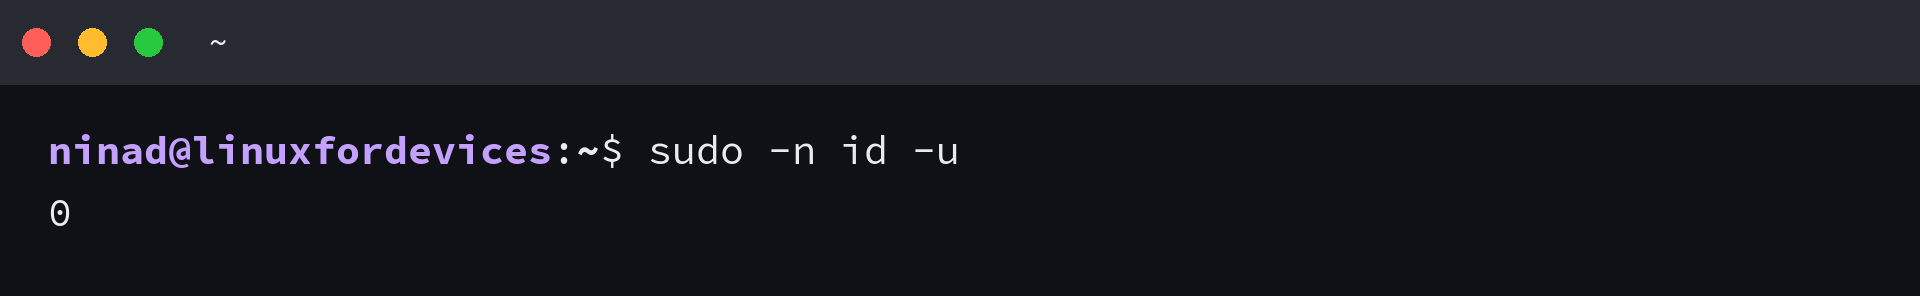
Use the same form with the administrative command you intend to run, and inspect its arguments before pressing Enter. A command with sudo receives the requested privilege for that command only. Your next shell command runs as your normal account.
Choose the user or shell
Use a single command when that is enough. Start a shell only when several commands genuinely need the same identity.
| Option | Effect | Use it when |
|---|---|---|
| -u nobody | Run as the named target account | A command must use that account’s permissions |
| -i | Start a login shell for the target user | The task needs that user’s login environment |
| -s | Start a shell using the current environment, adjusted by policy | You need a privileged shell and understand its inherited environment |
Both shell options target root by default.
The -i login mode initializes the target account’s environment. The -s option selects a shell without the same login setup, and environment filtering depends on sudoers policy. Do not assume either mode preserves every variable.
To run one command as a different account, specify that account with -u. The following command asks for the effective user name under the nobody account:
sudo -n -u nobody id -un
The output is nobody, the target account named in the command.
If you are checking administrative access, see how to find a user’s Linux groups. Creating a missing account is a separate task covered by the useradd command.
Change sudo access safely
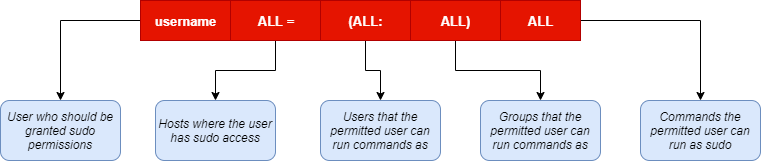
sudoers defines who can run which commands, on which hosts, and as which target users or groups. A rule ending in ALL grants broad command access.
Edit sudoers with visudo, which checks syntax before installing changes and helps prevent a malformed rule from locking administrators out.
alice ALL=(root) /usr/bin/systemctl restart example.service
This illustrative rule lets alice restart one named service as root. The executable path and arguments must match that system’s installation.
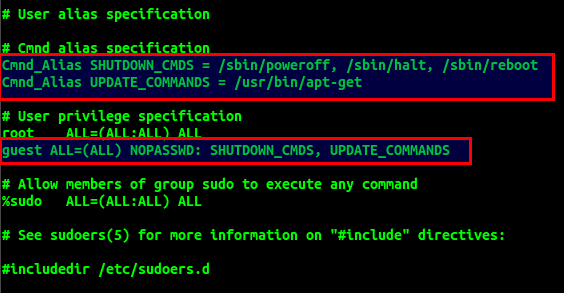
A command allowlist can still grant broad access. This image includes package management without a password, so package scripts may run with root privileges.
- Grant only the command the task requires, with a target user and arguments that fit the task.
- Avoid NOPASSWD unless the operational need and risk are understood.
- Validate the file with visudo before relying on the change.
Compare the privileges required for the shutdown command with package removal using apt, whose package scripts can execute with root privileges.
Keep elevation narrow
I prefer a one-command invocation when it completes the task because elevated access ends with that command. A root shell leaves every later command elevated.
sudo -n -l
Check the permissions before choosing the next administrative command. If the policy grants broader access than the task needs, ask its administrator to narrow the rule.
Sudo command FAQ
What does the sudo command do?
sudo asks the active security policy whether your account may run a command as a selected user, root by default. The policy may require authentication and may log the request.
Does sudo ask for the root password?
Authentication depends on the system’s policy. A common setup asks for the invoking user’s password, but a policy may use another method, cache credentials, or allow a command without a prompt.
What is the difference between sudo -i and sudo -s?
sudo -i starts a login shell for the target user. sudo -s starts a shell without the same login setup and uses the current environment as modified by policy.